Physical Espionage Marks Escalation in AI's Trillion-Dollar IP Race
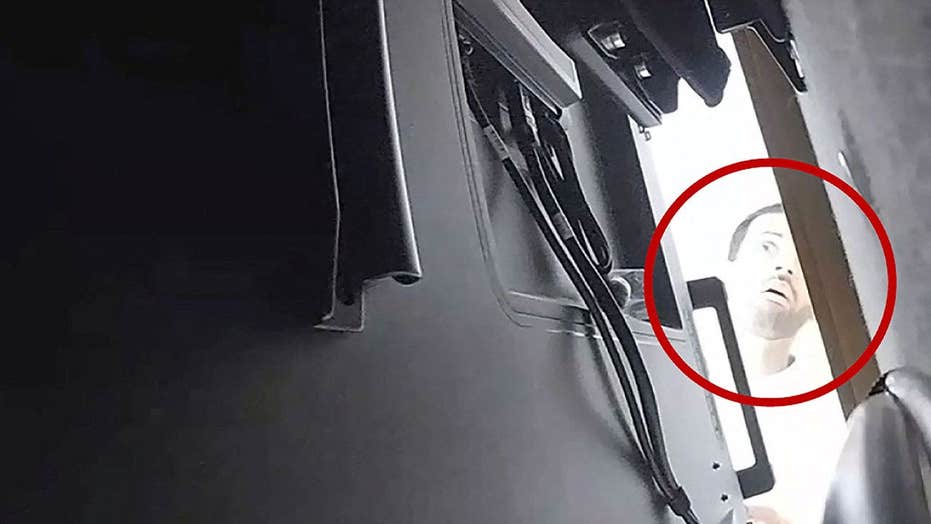
The indictment of a former AI engineer for allegedly bugging a corporate conference room escalates the AI sector's intellectual property wars from abstract code theft to tangible physical espionage. This incident transcends a simple security breach, framing the multi-trillion-dollar race for AI supremacy as a new cold war fought within company walls. It starkly highlights the vulnerability of open, collaborative tech campuses, a model now clashing with the immense strategic value of proprietary algorithms and training data. This act, if proven, signifies a critical escalation in corporate espionage tactics, demanding immediate C-suite attention. The mechanics of this alleged espionage reveal a critical failure in traditional physical and cybersecurity measures, which are often siloed. By placing a physical device, the engineer allegedly bypassed software-based monitoring focused on network traffic and data exfiltration, exploiting a low-tech seam in a high-tech environment. The primary losers are companies fostering "open innovation" cultures, like Google or Meta, which now face a strategic recalculation. Winners may be more traditionally siloed firms like Apple, whose culture of secrecy and hardware control provides a stronger defense against such insider threats, creating an asymmetric security advantage. The forward-looking implication is the rapid emergence of a new "counter-espionage" tech stack for the enterprise. Within 12 months, expect a surge in startups offering integrated physical-digital security solutions, from sophisticated audio detection systems to behavioral analytics that flag disgruntled employees. The critical variable will be whether these tools can be implemented without destroying the collaborative culture that drives innovation. This trajectory suggests enterprise security budgets are about to be fundamentally reallocated from a purely digital focus to a hybrid threat model, with CISOs now needing expertise in physical security.